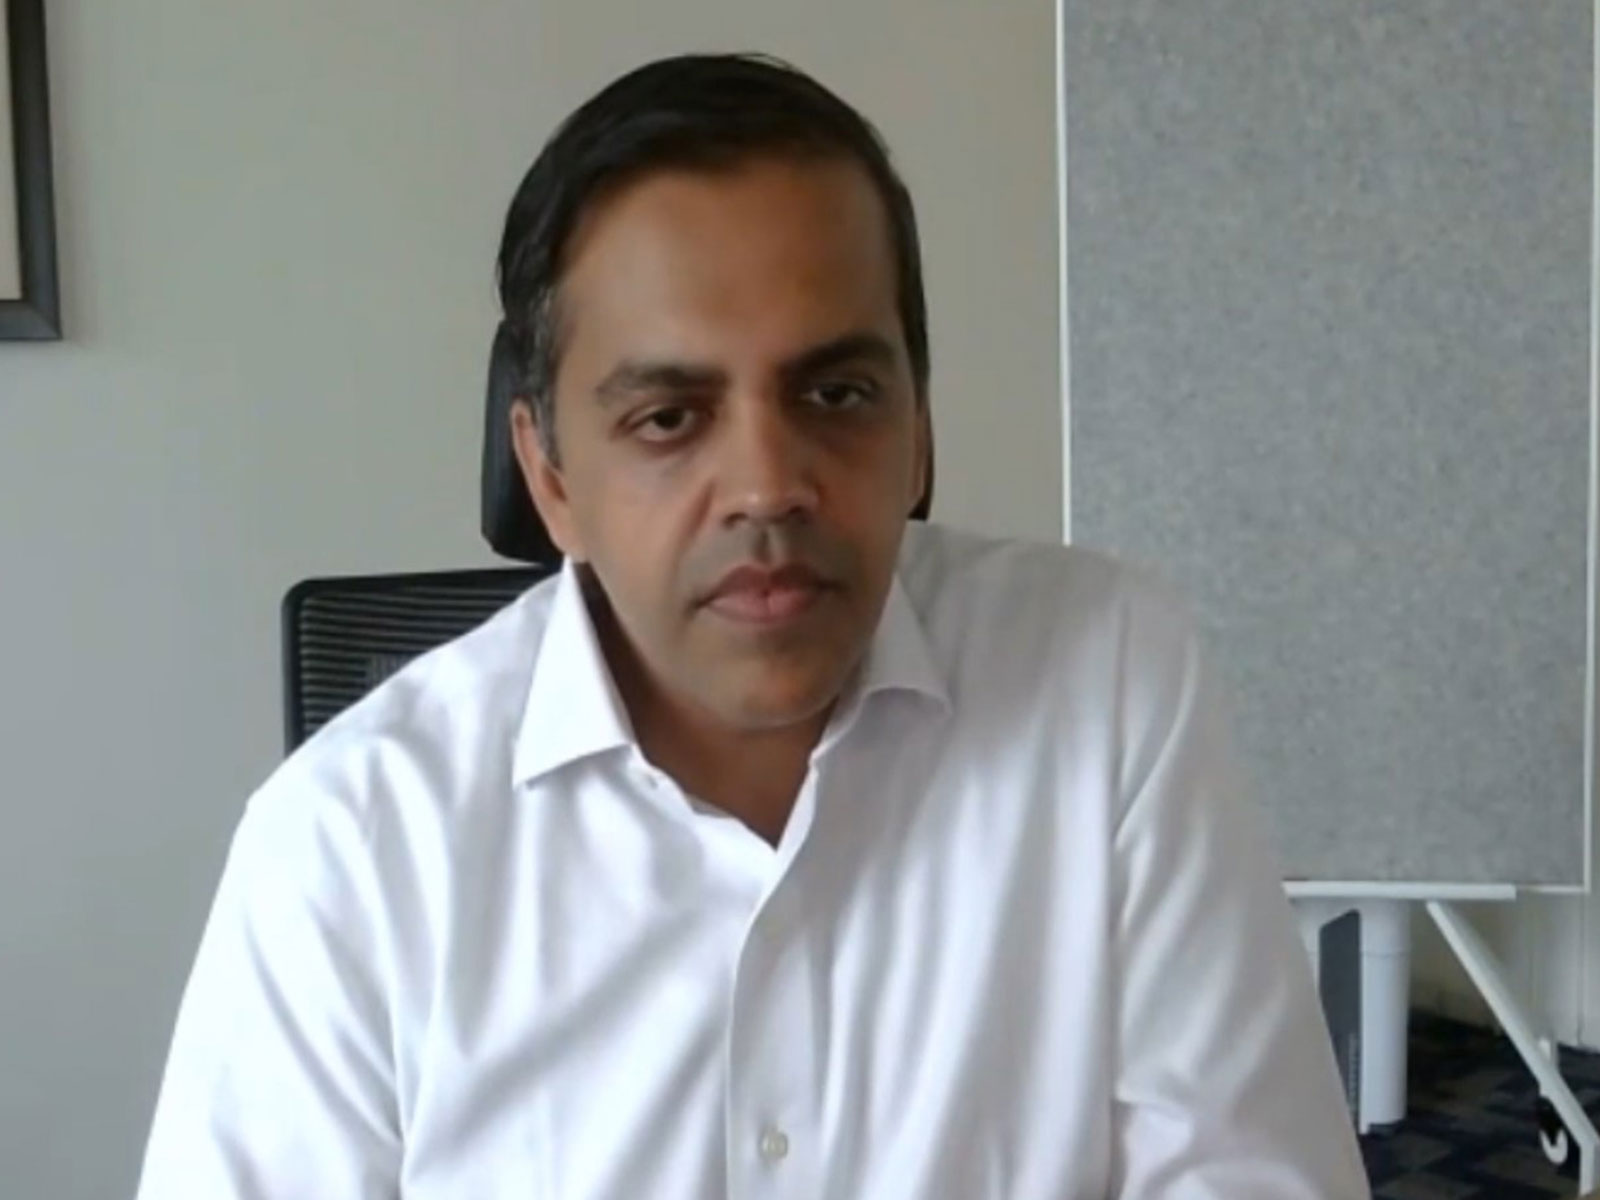
New Delhi [India], October 22 (ANI): Bengaluru-based digital trust and cybersecurity company eMudhra has attributed the security incident involving eight intermediate digital certificates to human error and a script failure, with Co-Founder Kaushik Srinivasan saying that no customer data breach or cyberattack occurred and that only a limited number of customers were directly affected.
Speaking to ANI, Srinivasan said the incident took place on April 30, 2025, when a script error during a routine key-generation process resulted in the creation of weak cryptographic keys. He acknowledged that the company lacked adequate manual checks to prevent the error.
"There was no infrastructure breach or data breach or anything. Uh, this was admittedly a human error caused by a script, you know, a sort of error that happened on April 30th, 2025, where these weak keys were created basically on hardware," Srinivasan said.
The incident involved eight intermediate Certificate Authority (CA) certificates associated with eMudhra's global website security business. The private keys linked to these certificates were found to be weak enough to be mathematically calculated, raising concerns that they could potentially be misused to create fraudulent certificates and impersonate legitimate websites.
Following the discovery, browser companies, including Google and Mozilla, took steps to distrust the affected certificates to reduce potential security risks.
Srinivasan said the key-generation process was routinely carried out by the company's team, but the incident exposed gaps in its internal controls.
"Now this key generation ceremony is a routine process for our team that has been performing it for a number of years. On that specific day this lapse happened," he said.
He added that adequate human-error checks and manual maker-checker controls were not in place when the weak keys were generated. The company is now reviewing the sequence of events to understand how the lapse occurred.
Srinivasan said the eight affected issuers had not issued certificates to end users. Seven had never entered production, while the one that did enter production had not issued identity certificates, he said.
"There was no customer, you know, data breach or anything of that sort, and no certificates were also issued to any customer from these issuers," he said.
The company, however, is working with customers affected by the distrust of its certificates. Srinivasan said one US customer had around 30,000 certificates associated with the affected Elliptic Curve Cryptography (ECC) route.
"There is one US customer under the ECC route with about 30,000 certificates," he said.
He added that the company's RSA route, through which the majority of certificate issuances take place, continued to be trusted by browsers.
In India, eMudhra is also considering moving some customers to alternative providers because of concerns about the incident, even though they have not been directly affected.
"In India there are a limited set of customers who are not directly affected, but obviously perception risk carries. So we are trying to migrate them to alternative providers," Srinivasan said.
He said the company was cooperating with browser programmes and responding to queries from the Ministry of Electronics and Information Technology (MeitY). According to Srinivasan, the ministry had clarified that India's Digital Signature Certificate (DSC) and eSign businesses were not affected.
To prevent similar incidents, eMudhra plans to strengthen its security and quality controls and explore automated tools, including Artificial Intelligence (AI), to supplement human checks.
"The main thing is to improve security controls and quality controls, right?" Srinivasan said.
The company is preparing an internal report explaining the incident and expects it to be ready within three to four days. It is also considering an independent review of its other keys, with plans to make the findings public.
Acknowledging the reputational impact, Srinivasan said rebuilding customer and investor confidence would take time. He said the company was communicating with investors who had contacted it to understand the incident, although it had not held a formal investor call. (ANI)
eMudhra attributes certificate security incident to human error, Co-Founder says few customers directly affected